 atisusanti
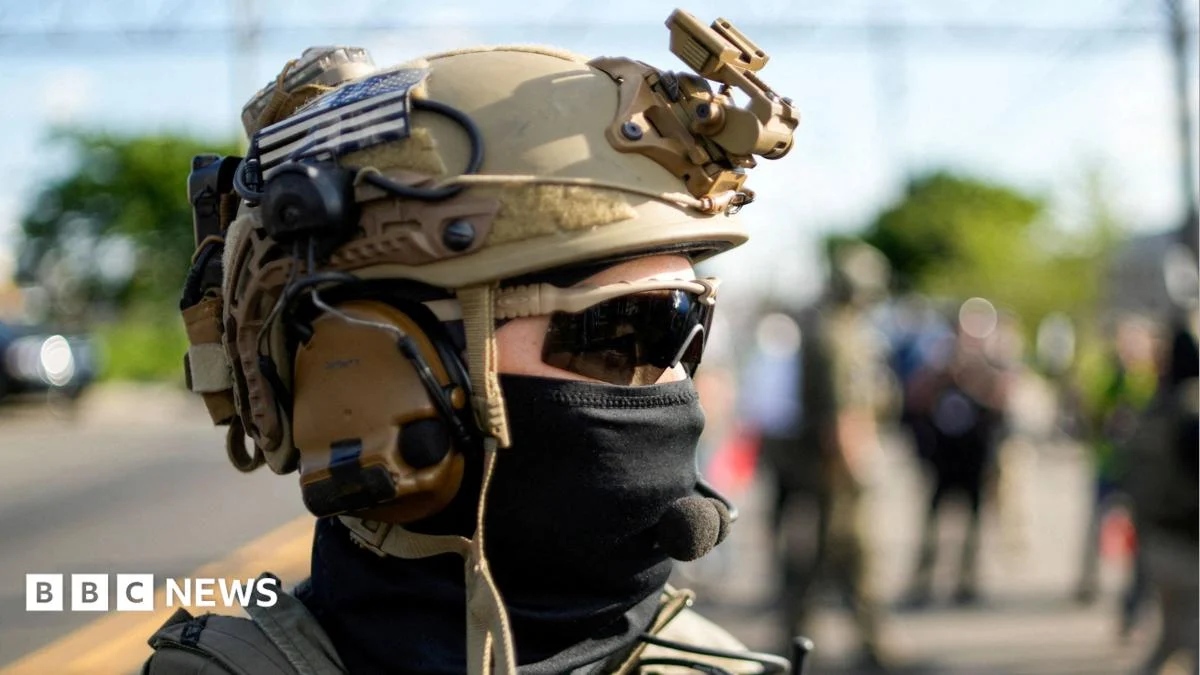
In a significant and deeply concerning data breach, details pertaining to over 41,000 personnel employed by the United States Department of Homeland Security (DHS) have been publicly disseminated. This extensive leak, which includes a substantial number of individuals directly involved in immigration enforcement, has exposed sensitive information such as names, work addresses, and phone numbers. The compromised data specifically affects agents working within the Immigration and Customs Enforcement (ICE) and Customs and Border Protection (CBP) agencies, and crucially, provides descriptions of the specific duties and responsibilities each individual undertakes within their respective roles. This incident marks the third major governmental data compromise in recent weeks, raising alarm bells about the security of sensitive federal information and the potential ramifications for national security and individual privacy.
The unprecedented breach, which placed the sensitive employee information online on Wednesday, was orchestrated by a collective known as the Department of Peace, in collaboration with prominent cybersecurity researcher and hacker, maia crimew. The leaked data has been compiled into a database, ominously titled "Icepick," and has been made accessible through a website hosted by Distributed Denial of Secrets (DDoSecrets), an organization known for its role in publishing leaked government documents. In a statement accompanying the release, the groups involved articulated their objective, asserting that the leak was not intended to function as a mere directory of DHS agents. Instead, their stated aim, as elaborated by Emma Best, a co-founder of DDoSecrets, was to "replace anonymity with accountability."
Emma Best further elaborated on the profound implications of this leak, describing it as "extraordinary but deceptive in its simplicity." She highlighted that the data specifically identifies officials responsible for overseeing a range of highly sensitive government operations. This includes individuals involved in covert and undercover operations, those tasked with the government’s efforts to identify and prosecute leaks, and key personnel implicated in the "failed BlueLeaks investigation." Moreover, the leak shines a spotlight on critical individuals within DHS’s "ever-escalating rendition and deportation programs," suggesting a deliberate effort to expose those at the forefront of controversial immigration policies.
The Department of Peace revealed on Wednesday that their access to these DHS agent profiles was gained through a single sign-on service known as Okta. Okta is a widely adopted online security tool utilized by numerous organizations to ensure that only authorized personnel can access internal platforms and systems. The implication is that a vulnerability within Okta’s single sign-on infrastructure may have been exploited, providing a gateway to the sensitive DHS data. In response to these claims, a spokeswoman for Okta acknowledged awareness of the allegations. However, the company maintained its security posture, stating, "Okta is secure, and we have no evidence our data or systems were compromised." This assertion, if accurate, suggests the compromise may have occurred at a different point in the data access chain, potentially within the DHS’s own systems or through a compromised individual account.
This latest incident follows a series of recent high-profile cyberattacks targeting government agencies. Last month, the Federal Bureau of Investigation (FBI) was the victim of a significant hack, where a group calling themselves ShinyHunters reportedly obtained personal information belonging to thousands of their agents. This breach raised concerns about the security of law enforcement personnel data. In the days immediately preceding the DHS leak, the Federal Election Commission (FEC), an agency responsible for overseeing political campaign finance and public disclosure of donation data, was taken offline due to a suspected hacking attempt. This pattern of escalating attacks on federal entities underscores a growing vulnerability and sophistication of cyber threats directed at U.S. government infrastructure.
The implications of the DHS leak are far-reaching and multifaceted. For the thousands of individuals whose personal and professional information has been exposed, the immediate concern is the risk of targeted harassment, intimidation, or even physical harm. Immigration enforcement agents, in particular, can be subject to heightened scrutiny and potential retribution, especially in the current polarized political climate surrounding immigration policies. The public dissemination of their roles and responsibilities could make them more vulnerable to retaliatory actions from individuals or groups who oppose their work.
Beyond the personal risks to individuals, the leak also poses a significant threat to ongoing law enforcement and national security operations. The detailed descriptions of the work performed by agents, especially those involved in covert or undercover capacities, could compromise sensitive investigations, endanger informants, and undermine the effectiveness of critical security measures. The exposure of personnel involved in rendition and deportation programs could also have international legal and diplomatic repercussions, potentially leading to accusations of human rights violations or violations of international law.
The involvement of groups like the Department of Peace and DDoSecrets, with their stated goal of promoting accountability, raises complex questions about the ethics and legality of such data releases. While proponents argue that transparency is essential for holding government agencies accountable for their actions, critics point to the potential for misuse of leaked information and the severe consequences for individuals whose privacy is violated. The debate over the balance between government transparency and individual privacy is likely to intensify in the wake of this incident.
The reliance on a single sign-on service like Okta as a potential vector for the breach also highlights the critical importance of robust cybersecurity practices across all levels of government. Even sophisticated security tools can be rendered vulnerable if not implemented and managed with the utmost diligence. The fact that a breach occurred despite the use of such a service suggests potential weaknesses in the DHS’s internal security protocols, employee training, or the overall security architecture of the systems connected to Okta.
The repeated targeting of government agencies in recent weeks signals a persistent and evolving threat landscape. Cybersecurity experts warn that such breaches are likely to continue unless significant investments are made in upgrading government IT infrastructure, enhancing employee cybersecurity awareness, and developing more proactive threat detection and response capabilities. The government’s ability to safeguard sensitive data is not only crucial for protecting its own operations but also for maintaining public trust and confidence in its capacity to govern effectively.
The Department of Homeland Security has yet to issue a comprehensive statement or detail the specific measures being taken to address the breach, mitigate its impact, and prevent future occurrences. As investigations into the leak unfold, the public will be looking for clear answers regarding how such a massive compromise was possible and what steps are being implemented to ensure the security of its personnel and sensitive data. The ramifications of this leak will undoubtedly be felt for some time, serving as a stark reminder of the pervasive and escalating challenges in the digital age of cybersecurity. The incident underscores the urgent need for a comprehensive review of federal data security protocols and a renewed commitment to protecting the information of those who serve the public. The "Icepick" database, now publicly accessible, represents a significant blow to the privacy and security of thousands of individuals, and a potential roadmap for those seeking to exploit governmental vulnerabilities. The ensuing fallout will likely involve extensive internal reviews, potential disciplinary actions, and a critical re-evaluation of the nation’s cybersecurity defenses.

 Roy Suryo
 Nana Banana
 Nakalama John
 Ramos Leo
