 Roy Suryo
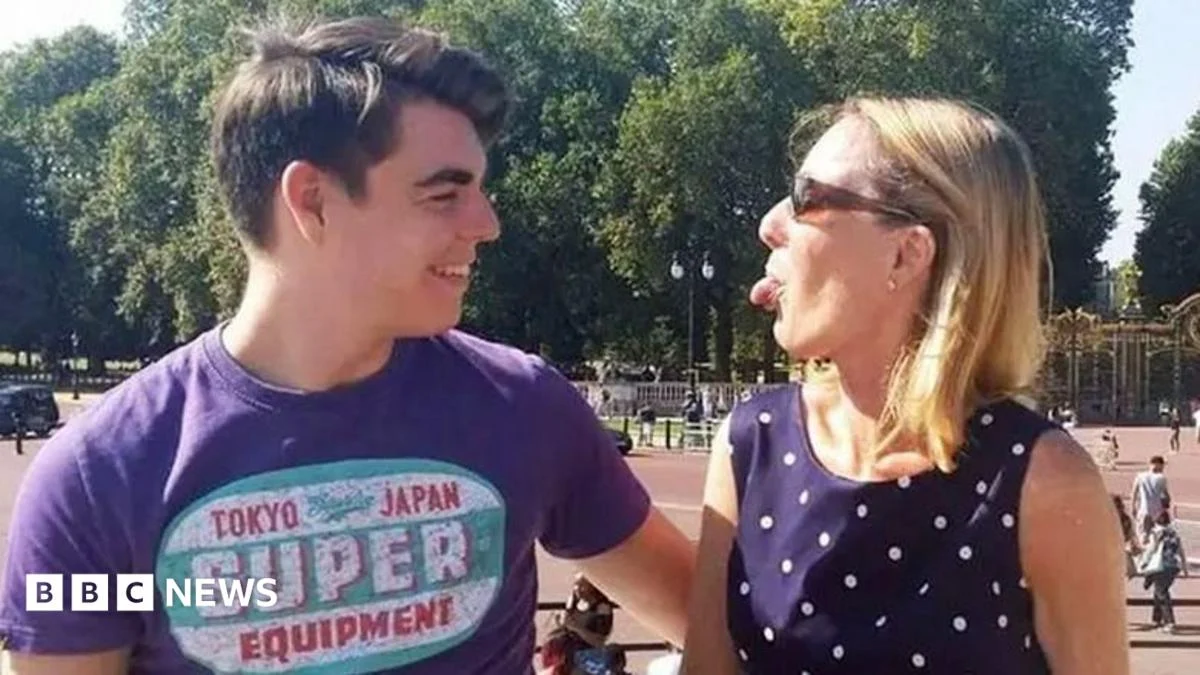
The mother of an 18-year-old autistic boy who died in hospital has expressed profound distress and hurt upon discovering that her son’s sensitive medical records may have been inappropriately accessed by NHS staff for years after his passing. Paula McGowan, whose son Oliver died in 2016 at Southmead Hospital in Bristol, was informed that at least five individuals employed by the Bristol Foundation NHS Trust had potentially accessed Oliver’s records without proper authorisation, with some instances occurring as recently as this year. The gravity of the situation has led to three nursing staff members being placed under formal investigation, while a doctor who has since departed the trust has proactively reported themselves to the General Medical Council (GMC), the UK’s regulatory body for doctors. A further member of staff is undergoing a separate review of their case. The trust has issued an apology for any emotional strain and anxiety this revelation has caused, and has also voluntarily referred the matter to the Information Commissioner’s Office (ICO), the UK’s data protection watchdog, for independent scrutiny.
This distressing incident is the latest in a growing number of concerns surrounding NHS staff accessing patient records without a legitimate professional justification. In July, Sir Jim Mackey, the head of NHS England, issued a stern and unambiguous warning, stating that any staff found to be improperly accessing patient data could face severe consequences, including dismissal from their posts and even potential imprisonment. Recent high-profile cases that have highlighted these vulnerabilities include unauthorized access to the medical records of victims involved in the horrific attacks in Nottingham and Southport, as well as the case of a child injured in a crocodile enclosure in Cambridgeshire. The scale of the problem was further underscored this month by an investigation conducted for the Health Services Journal. This inquiry revealed a deeply concerning trend, indicating that at least 214 NHS staff members have lost their jobs and approximately 2,000 have faced disciplinary sanctions for snooping on sensitive patient data over the past five years alone.
Oliver, who was diagnosed with a mild learning disability and suffered from epilepsy, tragically died in 2016 at Southmead Hospital. His death followed the administration of anti-psychotic medication, a course of treatment his family had repeatedly and vehemently warned against, believing it was unsuitable for him. Following Oliver’s death, Ms. McGowan, in her pursuit of information and understanding, requested access to his medical records. The subsequent review revealed a startling figure: 38 individuals had accessed Oliver’s data since his death. During this period, a total of 637 distinct items from his records were viewed, and 67 were printed. The trust has stated that the majority of this access was deemed appropriate, primarily linked to the handling of complaints, ongoing legal proceedings, and the crucial coroner’s inquest into Oliver’s untimely demise.
However, the investigations have identified three nursing staff members who were not directly involved in Oliver’s care and are now under formal investigation. Initial inquiries have been unable to provide any evidence that these individuals had a legitimate professional reason to view her son’s sensitive medical information. A fourth staff member’s case is also being reviewed separately. Ms. McGowan recounted being informed that one nurse expressed a general interest in anti-psychotic drugs and the care of patients with learning disabilities as a reason for accessing Oliver’s files. This justification has raised significant questions about the boundaries of professional curiosity and the protection of patient confidentiality. The trust is also actively examining 13 other cases involving former staff, including doctors, nurses, and clerical workers, to ascertain whether their access to patient records was appropriate. In one notable instance, a doctor who is no longer employed by the trust has proactively referred themselves to the GMC after being contacted by the hospital regarding their access to Oliver’s records.
Bristol NHS Foundation Trust has acknowledged the seriousness of the situation, stating that it is conducting a "thorough investigation" and that it would be "inappropriate to reach conclusions before those enquiries are complete." Professor Steve Hams, the trust’s chief nursing and improvement officer, emphasized the fundamental right of every patient and family to expect that their personal information will be handled with the utmost care, respect, and confidentiality. He added, "Any concern that records may have been accessed without a legitimate reason is something we take extremely seriously." The trust has reiterated its commitment to taking "appropriate action through the relevant processes" should any instances of staff misconduct be identified.
NHS medical records are repositories of highly sensitive personal information, encompassing a wide spectrum of details. This can include confidential test results, comprehensive hospital discharge summaries, detailed prescription information, and medication histories. The scope of information contained within these records extends far beyond what is readily accessible to patients through platforms like the NHS app. It can also include sensitive details related to safeguarding concerns, thorough risk assessments, crucial correspondence exchanged between healthcare professionals, and detailed consultation notes from appointments.
It is important to note that there is not a single, unified NHS-wide electronic record system that grants all staff unfettered access. Instead, healthcare organisations, including individual GP practices, hospitals, and specialist clinics, maintain their own distinct record-keeping systems. These organisations are responsible for establishing and enforcing policies that dictate who can access specific types of patient information. While doctors, nurses, and other healthcare professionals frequently require swift access to patient records, particularly in emergency situations, they are bound by a strict ethical and legal obligation to only view confidential information when there is a legitimate, work-related reason and they possess the appropriate authorisation.
Modern IT systems are designed to maintain a comprehensive audit trail, which meticulously records every instance of access to a patient’s records, including the identity of the individual accessing the data and the precise time of access. This audit trail is a critical tool for ensuring accountability and investigating potential breaches of confidentiality. NHS England has been unequivocal in its stance, stating that any instance of staff accessing records without a valid reason would be considered "wholly unacceptable, a disgraceful breach of patients’ trust and against the law." A spokesperson further reinforced this message, stating, "We have been crystal clear that staff could face disciplinary action for any breaches, including the loss of their job and potential criminal prosecution." The ongoing investigations at Bristol Foundation NHS Trust underscore the persistent challenges in safeguarding patient data within the NHS and the vital importance of maintaining robust oversight and accountability mechanisms.

 Nakalama John
 George Anjay