
 Nakalama John
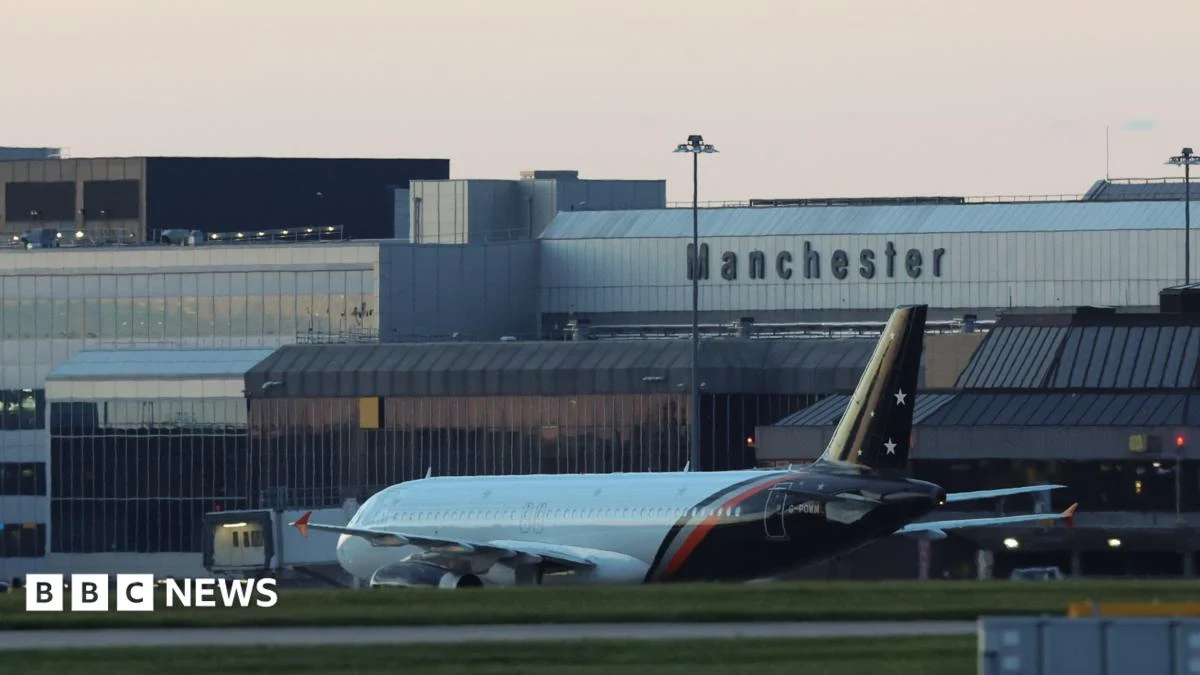
Michael Goddard, a 71-year-old resident of Cheshire, was among the first wave of individuals to receive an unsettling email from MAG, notifying him and his 68-year-old wife, Julie, that their personal data had been compromised. "I was shocked," Goddard recounted to BBC Radio Manchester, expressing a sentiment echoed by countless others now grappling with the implications of the breach. "To find your personal info has been stolen – it is alarming." The realization that his private details were now in the hands of unknown malicious actors left Goddard feeling deeply unsettled and uncertain about the future. His immediate concern revolved around the potential misuse of the information, given the ease with which such data can be exploited.
Goddard articulated his unease regarding the breadth of the stolen information, noting, "My information has gone and I don’t know what they’re going to do with it." He elaborated on the specific details he knew to be compromised: "They have my address in the form of the postcode, they’ve got my name, so it doesn’t take too much to find out who I am." This basic combination of name and postcode, while seemingly innocuous, forms a crucial foundation for more elaborate social engineering attacks, phishing scams, and even direct identity theft. For individuals like Goddard, who value their privacy and security, the breach represents a profound violation and a source of considerable stress. The partial reassurance offered by Manchester Airports Group has, according to Goddard, fallen short of alleviating his profound worries, leaving him "not 100% reassured" by their public statements.
The specific circumstances leading to the Goddards’ data compromise highlight the varied touchpoints through which customers interact with airport services. Michael Goddard’s information was exposed following his travel from East Midlands Airport earlier this year, suggesting that travel booking systems or associated databases might have been targeted. Concurrently, his wife Julie’s data was affected due to her use of the online booking service for parking at Manchester Airport, indicating that separate but interconnected systems could have been breached. This dual exposure from different services underscores the pervasive nature of the attack and the potential for a wide array of customer data, accumulated through diverse interactions, to have been accessed. "The concern is there for both of us," Goddard stressed, highlighting the shared anxiety experienced by couples and families caught in the wake of such a breach. Their primary demand, shared by many, is for concrete assurance: "We want the reassurance that if anything happens, they will adequately compensate us."
Manchester Airports Group has confirmed that the identity of the hackers responsible for this extensive cyberattack is known to them. This crucial detail suggests that law enforcement agencies and cybersecurity experts are actively involved in the investigation, potentially working towards attribution and prosecution. MAG stated that all relevant authorities have been informed, a standard procedure in such high-profile incidents involving critical infrastructure. While the specific identities or affiliations of the perpetrators have not been publicly disclosed, the knowledge of their identity could be a significant step towards understanding the motive behind the attack, whether it be financial gain, state-sponsored espionage, or hacktivism. The complexity of cybercrime attribution often involves intricate digital forensics and international cooperation, making MAG’s declaration a notable development.
In response to the severity of the incident, the Information Commissioner’s Office (ICO), the UK’s independent authority set up to uphold information rights, has initiated an assessment of the breach. A spokesperson for the ICO confirmed, "We can confirm we have received a breach report from Manchester Airports Group, and we are assessing the information provided." This assessment process typically involves a thorough review of the circumstances surrounding the breach, the nature and volume of the data compromised, the security measures in place at MAG, and the company’s response strategy. The ICO possesses significant powers under the General Data Protection Regulation (GDPR) and the Data Protection Act 2018, including the ability to impose substantial fines on organisations that fail to adequately protect personal data. For individuals impacted by the breach, the ICO serves as a crucial resource, providing guidance and support. The organisation specifically directed those concerned by the breach to access support resources available on the ICO website, offering practical steps individuals can take if they’ve been affected by a personal data breach.
The potential ramifications for millions of UK airport customers extend far beyond immediate shock and alarm. The theft of personal data, even seemingly basic details like names and postcodes, can serve as a gateway for more sophisticated cybercrimes. Fraudsters often use such information to build comprehensive profiles of their targets, which can then be leveraged for identity theft. This might involve opening new credit accounts in victims’ names, applying for loans, or even filing fraudulent tax returns. Phishing attacks are another significant threat, where criminals use the stolen data to craft highly convincing emails or messages designed to trick individuals into revealing further sensitive information, such as bank account details or passwords. These scams can be incredibly difficult to detect, especially when the perpetrators possess accurate personal information, making their communications appear legitimate.
Financial fraud is a direct and pressing concern for many victims. While MAG has not publicly confirmed the compromise of payment card details, the possibility always exists in large-scale breaches. Even without direct payment information, fraudsters can exploit personal data to gain access to existing accounts or to facilitate other forms of financial exploitation. The long-term psychological impact on victims should also not be underestimated. The constant vigilance required to monitor bank accounts, credit reports, and unsolicited communications for suspicious activity can be incredibly stressful and time-consuming. Many individuals report feeling a pervasive sense of unease and a loss of trust in digital services following a data breach, fundamentally altering their online behaviour.
The legal framework surrounding data protection in the UK, primarily the GDPR, empowers individuals with significant rights when their personal data is mishandled. Under GDPR, organisations are mandated to implement appropriate technical and organisational measures to ensure a level of security appropriate to the risk. Failure to do so can lead to severe penalties, as determined by the ICO. Affected individuals may also have the right to seek compensation for damages incurred as a result of the breach, including both financial losses and non-material damage such as distress. The possibility of class-action lawsuits or group litigation orders is often explored in breaches of this magnitude, allowing multiple victims to collectively pursue claims against the responsible organisation. Such legal avenues provide a mechanism for victims to seek redress and for organisations to be held accountable for their data protection failings.
This incident at Manchester Airports Group is part of a broader, troubling trend of escalating cyberattacks targeting critical infrastructure and major corporations globally. Airports, as vital hubs for travel and commerce, represent particularly attractive targets for cybercriminals, whether they are financially motivated gangs, state-sponsored actors seeking intelligence, or hacktivists aiming to disrupt. The interconnected nature of modern travel systems, encompassing everything from booking and baggage handling to air traffic control, presents a vast attack surface for malicious actors. Organisations like MAG face immense pressure to continually upgrade their cybersecurity defenses to counteract increasingly sophisticated threats, often operating within a complex ecosystem of third-party vendors and legacy systems that can introduce vulnerabilities. The challenge is not merely to prevent breaches but to develop robust incident response plans that minimize harm and provide transparent communication to affected parties.
In the aftermath of such a significant compromise, Manchester Airports Group will undoubtedly face intense scrutiny regarding its cybersecurity practices and its commitment to customer data protection. Rebuilding customer trust will be a formidable task, requiring not only transparent communication about the incident and ongoing investigation but also demonstrable improvements in security infrastructure. This might include enhanced encryption protocols, multi-factor authentication for all customer-facing services, regular security audits, and increased investment in cybersecurity personnel and technologies. For the millions of UK airport customers, the breach serves as a stark reminder of the digital risks inherent in modern life and the critical importance of personal vigilance. Changing passwords, enabling two-factor authentication, carefully monitoring financial statements, and being wary of unsolicited communications are now essential practices for safeguarding one’s digital identity in an increasingly vulnerable online world. The ongoing assessment by the ICO and the promise of investigating the hackers’ identity offer some hope for accountability, but the immediate burden of protection falls heavily on the individuals whose data has been exposed.

 George Anjay
 atisusanti
 Ramos Leo
 Roy Suryo
 Nana Banana
