 atisusanti
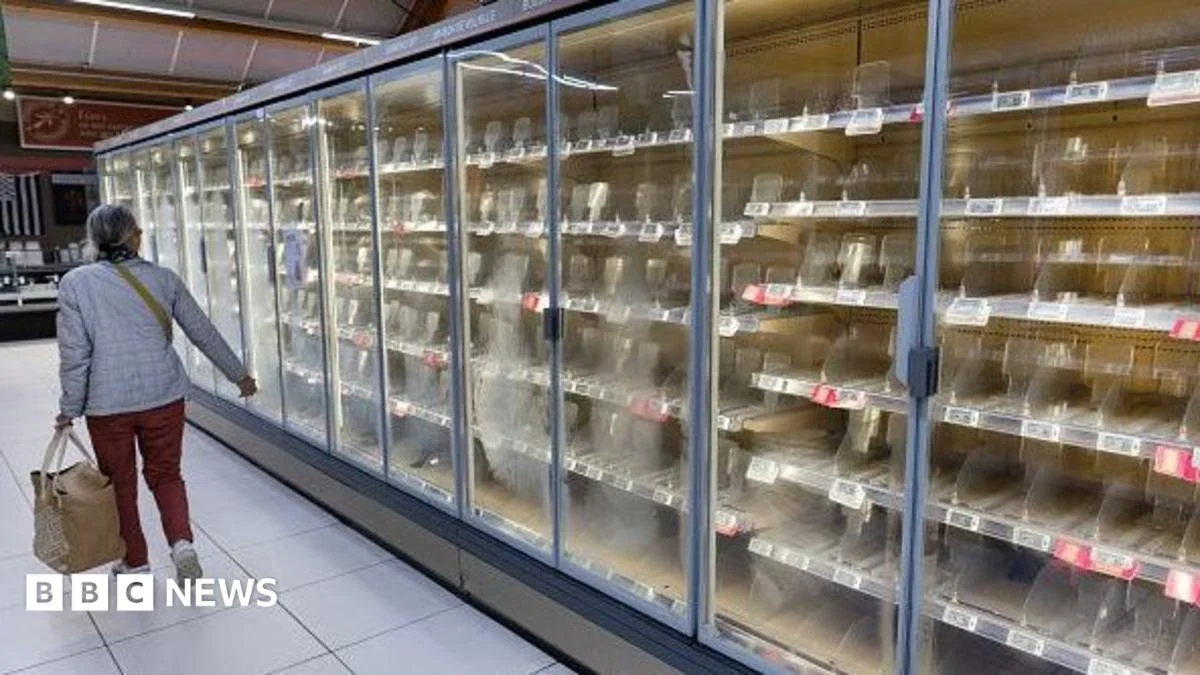
Supermarkets across Europe have recently found themselves at the forefront of a chilling cybersecurity crisis, as a suspected cyber-attack targeted their refrigeration systems, plunging the sector into a state of alarm and igniting widespread concern about the inherent vulnerabilities of internet-connected hardware. This incident serves as a stark reminder that the digital tendrils of the internet now extend far beyond our personal computers and smartphones, reaching into the very infrastructure that underpins our daily lives, from the complex machinery of industrial plants to the seemingly innocuous domestic appliances that populate our homes. The ramifications of such breaches, as evidenced by the supermarket freezer hack, are no longer confined to data theft or service disruption; they can manifest as tangible, physical consequences, impacting everything from the integrity of our food supply to the operation of critical infrastructure.
The proliferation of smart devices, interconnected and accessible via the internet, has become a defining characteristic of modern living. From smart refrigerators that can track inventory and suggest recipes to sophisticated central heating systems that optimize energy consumption and washing machines that can be programmed remotely, these devices promise unparalleled convenience and efficiency. However, this interconnectedness, while theoretically enabling seamless remote control, also opens a Pandora’s Box of potential security risks. Any device that ventures onto the digital highway, no matter how mundane its function, becomes a potential entry point for malicious actors seeking to exploit vulnerabilities.
While the prospect of hackers gaining control of everyday appliances might sound like a plot from a science fiction thriller, it is a very real and present danger. However, it is crucial to temper this alarm with a dose of reality: the notion that hackers can effortlessly commandeer any connected device is an oversimplification. Reputable manufacturers, particularly those dealing with high-stakes sectors, generally invest significant resources and expertise into fortifying their technology against such threats. Robust security protocols, encryption, and regular patching are standard practices aimed at creating a formidable barrier against unauthorized access.
Nevertheless, the history of cybersecurity is replete with instances where even well-established brands have fallen victim to exploit. As far back as 2015, researchers demonstrated a concerning vulnerability in a Samsung smart fridge that could have allowed them to intercept internet traffic, highlighting how even seemingly minor flaws in complex systems can have significant security implications. This incident, while not directly linked to the recent supermarket attacks, underscores the persistent challenge of ensuring comprehensive security across the ever-expanding landscape of connected devices.
It is important to note that there is currently no direct evidence to suggest that domestic appliances were the specific targets in the recent cyber-attacks that crippled supermarkets in November. The focus of these attacks appears to have been on the operational technology (OT) systems within the retail environment, specifically those controlling critical functions like refrigeration. However, the broader implications for the security of interconnected devices remain a paramount concern.
Ciaran Martin, former chief executive of the UK’s National Cyber Security Centre (NCSC), has voiced a strong call to action for manufacturers, emphasizing their responsibility to elevate the security standards of connected devices. "There’s a lot more that we need to demand of big tech to give us safer devices and products in the first place," he stated, underscoring the need for a proactive approach to security rather than a reactive one. Consumers, too, have a role to play in bolstering their digital defenses. Martin advised individuals to diligently keep their devices updated with the latest security patches and to enable multi-factor authentication wherever possible. While he acknowledges that these steps can be perceived as an inconvenience, he stresses that "it only takes a few seconds" and can significantly mitigate risk.
Recognizing the growing threat, the UK has taken legislative steps to address the security of smart devices. Since April 2024, manufacturers of certain consumer smart devices are legally mandated to adhere to minimum cybersecurity standards. These regulations encompass crucial requirements such as robust password policies and the provision of timely security updates, aiming to create a baseline level of protection for consumers.
The NCSC has been actively engaged in understanding the intricacies of the supermarket incidents, collaborating with international partners and industry stakeholders. While the NCSC stated it was unaware of any direct impact on the UK from these specific attacks, a recent investigation by researchers from UK Cyber Defence has unearthed a potentially worrying discovery. They identified over 800 refrigeration and building-control interfaces associated with British retailers that are accessible via the public internet. While accessibility does not automatically equate to vulnerability, it does expose these systems to potential risks, particularly if they are secured by weak passwords or suffer from unpatched software vulnerabilities.
The gravity of such threats has not gone unnoticed by the UK government. Following earlier attacks on supermarkets, the government has already initiated discussions with senior food retailers to enhance their cyber resilience. Helen Dickinson, chief executive of the British Retail Consortium, has echoed these concerns, labeling cyber incidents as a "major concern for retailers." The industry is actively collaborating with the NCSC, sharing vital intelligence and collectively strengthening their defensive postures.
This is not the first instance where cyber-attacks have cast a shadow over the integrity of the food supply chain. In May 2025, UK supermarkets M&S and the Co-op were targeted by ransomware hackers, leading to significant disruptions in their operations. The retailers struggled to restock shelves with fresh deliveries, resulting in widespread customer complaints of empty aisles across the UK in the days following the attacks. These past events serve as a potent precursor to the current concerns, demonstrating the tangible and far-reaching consequences of compromised retail IT systems.
Tom Hegel, a researcher at cybersecurity firm SentinelOne, has pinpointed a critical question that retailers must address: "The question retailers need to answer is who owns the security of that equipment, not just who repairs it." This highlights a systemic issue where the responsibility for maintaining the security of connected operational technology is often unclear, leading to potential gaps in defense. He further elaborates that while internet connectivity offers undeniable advantages in terms of convenience, the pace of security advancements has not always kept pace with the rapid integration of these technologies.
"Once an attacker can operate those controls, legitimate functions such as defrosting become tools for disruption," Hegel warns. This is a particularly alarming prospect, as it transforms everyday operational tools into weapons of sabotage. "Changing a setting can destroy physical stock, not just interrupt a computer system," he emphasizes, painting a vivid picture of the potential for devastating physical damage orchestrated through a digital breach.
Beyond the confines of the retail sector, the implications of unsecured connected technology extend to a far broader spectrum of critical infrastructure and everyday life. The interconnectedness that enhances convenience in our homes and workplaces also permeates industries responsible for essential services and personal mobility.
The potential for vulnerability extends to sectors such as the automotive industry, power generation, and water supply networks. Cyber security expert Ken Munro points to a significant past incident that serves as a potent cautionary tale. In 2015, researchers demonstrated the alarming ease with which a Jeep could be remotely hacked through its internet-connected entertainment system. This exploit, which allowed for remote control of critical vehicle functions, prompted a widespread wake-up call within the automotive industry, leading to significant improvements in vehicle security protocols. "Fortunately, the vehicle industry woke up to this and fixed the problem," Munro stated, acknowledging the industry’s response but also implicitly highlighting the latent risks that existed.
In the realm of utilities, mobile connections are widely employed to monitor and manage critical equipment in power plants and water networks, enabling engineers to oversee operations remotely and efficiently. Munro notes that while UK utilities generally exhibit a strong commitment to securing these connections, the standards of security can vary significantly across different regions and countries. His primary concern lies with smaller, less well-funded utility companies that may still be reliant on older, inherently vulnerable equipment, creating potential weak points in the national infrastructure.
The risks associated with unsecured connected technology are not limited to specialized industrial applications. Olivier Daloy, a cybersecurity expert at Zscaler, articulates a broader concern: "any factory or equipment" connected to the internet, regardless of its sector – from car manufacturers to electricity grids and transportation infrastructure – could face similar threats. This underscores the pervasive nature of the challenge and the need for a holistic approach to cybersecurity that addresses the interconnectedness of modern systems. The supermarket freezer hack, while seemingly a localized incident, serves as a potent harbinger of broader vulnerabilities that demand urgent attention across all sectors of our increasingly digital world. The convenience offered by connected technology must be meticulously balanced with robust and evolving security measures to prevent these innovations from becoming instruments of disruption and damage.

 Ramos Leo
 Nana Banana
 Roy Suryo
 George Anjay
 Nakalama John
