 atisusanti
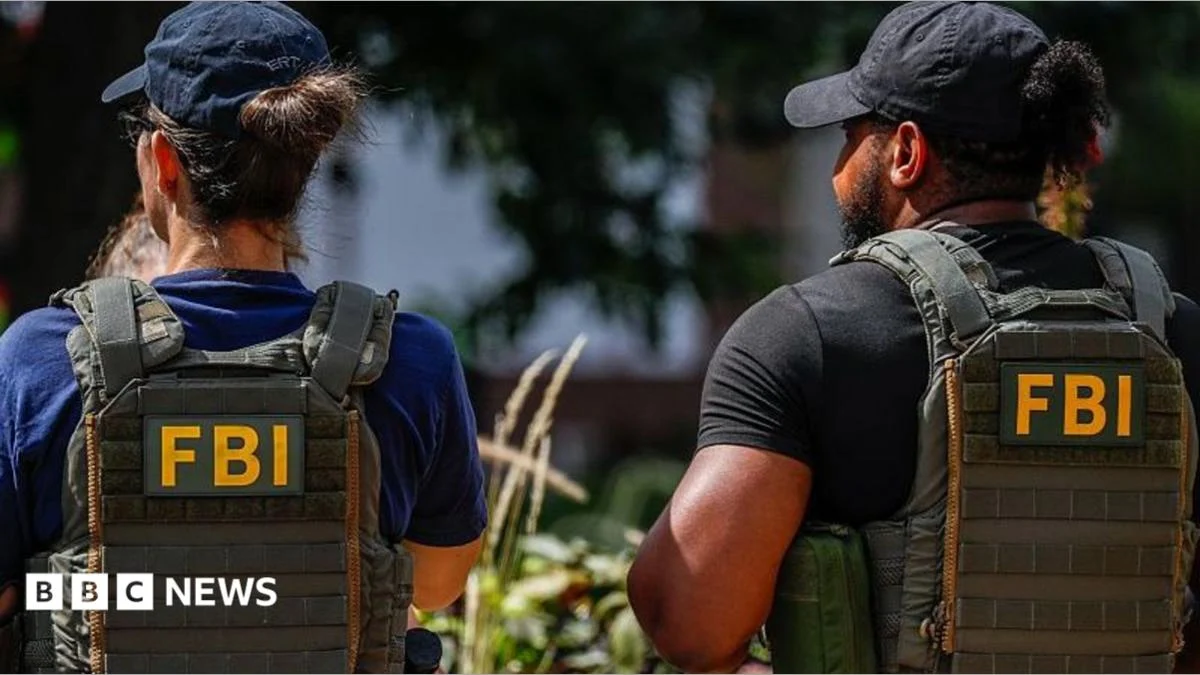
Cyber-criminals claiming allegiance to the notorious hacking collective ShinyHunters have asserted they have successfully infiltrated FBI systems, exfiltrating an alarmingly vast and exceptionally sensitive trove of medical data belonging to thousands of its special agents. BBC News has independently verified samples of this compromised information, which appears to be derived from "fitness-for-work" medical examinations. These records contain highly personal details, including specific blood and urine test results, as well as candid doctors’ notes that detail a spectrum of medical conditions. Among the disclosed ailments are seemingly innocuous, yet still private, details such as a "shellfish and banana allergy," alongside more concerning medical flags like "blood in the urine" and diagnoses of "high cholesterol." The exposed data extends beyond mere test results, encompassing agents’ full names and residential addresses, painting a stark picture of the personal vulnerabilities now laid bare.
The potential ramifications of this data breach are dire and far-reaching, according to cybersecurity experts. They warn that the stolen information could render FBI agents susceptible to a wide array of malicious activities, including sophisticated phishing scams, targeted blackmail operations, and even dangerous impersonation attempts by criminals seeking to pose as law enforcement officers. "The list maps thousands of agents against their medical and fitness records," stated Etay Maor, vice-president of threat intelligence at Cato Networks. "Passwords can be reset if stolen, but medical records cannot, so once this data is out, it stays compromised for good. That permanence, applied across an entire workforce, is what makes this leak so serious." This emphasis on the irretrievable nature of medical data underscores the gravity of the situation.
While the FBI has been reticent to offer extensive comment, on Wednesday, the agency officially acknowledged the breach, issuing a statement that it was "aggressively investigating" the incident and the methods employed by the perpetrators. The cyber-criminal group ShinyHunters, however, has been more vocal. They claim to have initiated their breach on Monday and subsequently publicized details of their attack on their darknet site. In a move that has raised eyebrows, the group also shared samples of the allegedly stolen data with various media outlets, accompanied by an unusual extortion demand.
The demand itself deviates from typical ransomware scenarios. Instead of financial compensation, ShinyHunters is reportedly seeking a retraction of an FBI advisory published in May, which they claim "offended" them. This peculiar motivation adds another layer of complexity to an already alarming situation. The samples provided to journalists appear to be authentic, containing a wealth of personal identifiers. These include not only agents’ names and addresses but also their phone numbers, badge numbers, job titles, and even sensitive information about their spouses. Preliminary analysis suggests that the compromised records pertain to thousands of agents, potentially including high-ranking officials such as deputy directors, indicating a broad sweep of the agency’s personnel.
Professor Ciaran Martin, the former head of the UK’s National Cyber Security Centre, has characterized the hack, if confirmed, as "as serious as it gets when it comes to data breaches." His assessment highlights the significant threat posed to national security and individual privacy. Further reporting by Reuters has shed more light on the specific nature of some of the exposed data, revealing that it includes information on agents actively involved in sensitive investigations. These investigations reportedly concern adversaries such as Russia and China, as well as high-profile drug cartels. The exposure of such intelligence could have profound implications for ongoing operations and the safety of the agents involved.
Adding to the complexity of the breach, reporting by 404 Media suggests that details of a previously little-known FBI hacking unit, responsible for remote operations, may also have been exposed. This revelation raises concerns about the potential compromise of the FBI’s own offensive capabilities and the information it holds on its clandestine operations. Initially, it was believed that the breach might have affected the FBI’s entire workforce of 38,000 current employees. However, ShinyHunters has since escalated their claims, asserting that the scale of the data theft is considerably larger. The group now alleges to possess sensitive information on approximately 60,000 current and former FBI staff, indicating a significant underestimation of the breach’s scope by the agency or the hackers themselves.
Jamie Akhtar, chief executive and co-founder of CyberSmart, while urging caution regarding the hackers’ claims, has nonetheless described the breach as "extremely concerning." He elaborated on the potential misuse of such sensitive data: "Such data could be used for highly convincing phishing, impersonation, identity fraud, blackmail or even operations targeting law-enforcement personnel, making the potential implications particularly serious." This underscores the multifaceted threats posed by the exfiltration of personal and medical information.
The hackers, who communicate with reporters in English via the messaging service Telegram, have issued an ultimatum: they intend to publish the full dataset in five days unless the FBI accedes to their demands for the retraction of the advisory. ShinyHunters is an established international hacking collective, active since 2019, and has been implicated in numerous high-profile cyber-attacks. Their previous targets include significant incidents affecting Rockstar Games, the developer of the Grand Theft Auto franchise, and the educational platform Canvas, underscoring their capability and reach.
According to the hackers’ account, they exploited a vulnerability in an Oracle cloud storage system utilized by the FBI. This exploit reportedly granted them access to multiple critical FBI platforms. Among the compromised systems are FBIJobs, the portal for employment applications; FBI BEAST, which manages background checks for employees and applicants; FBI MedLink, the system storing sensitive medical records; and FBI BICS, a database containing investigative information. The interconnectedness of these systems highlights how a single point of vulnerability can cascade into widespread data compromise.
In a statement released on the social media platform X, formerly Twitter, the FBI acknowledged its ongoing efforts to ascertain whether the hackers had directly breached its systems or had compromised a third-party provider. The statement read: "We are actively and aggressively investigating this matter and working closely with those third-party providers that support FBIJobs.gov to mitigate any and all risk." This admission of uncertainty regarding the precise vector of the attack underscores the challenges faced by the agency in responding to sophisticated cyber threats. The protracted nature of the investigation and the potential for further revelations from ShinyHunters loom large over the FBI, raising critical questions about its cybersecurity posture and the protection of its personnel’s most private information. The incident serves as a stark reminder of the persistent and evolving threats in the digital realm, particularly for organizations entrusted with sensitive national security and personal data.

 George Anjay
 Roy Suryo
 Nakalama John